Digital infrastructure forms the backbone of any modern organization, yet many companies build their networks on foundations full of invisible cracks. A single unpatched server or a weak password can compromise years of hard work within minutes. Protecting this digital environment requires more than installing standard antivirus software or relying on default firewall settings. Real defense demands active probing, continuous testing, and a deep understanding of how malicious actors operate inside complex networks.
Organizations often assume their systems are safe simply because they have not experienced a public breach yet. This false sense of security leads to neglected updates, poorly configured cloud storage buckets, and overlooked software vulnerabilities. Attackers scan the internet constantly, looking for these exact oversights. When they find an entry point, they move laterally through the network, exfiltrating sensitive data or locking down operations with ransomware before anyone notices.
Uncovering Hidden Weaknesses Through Penetration Testing
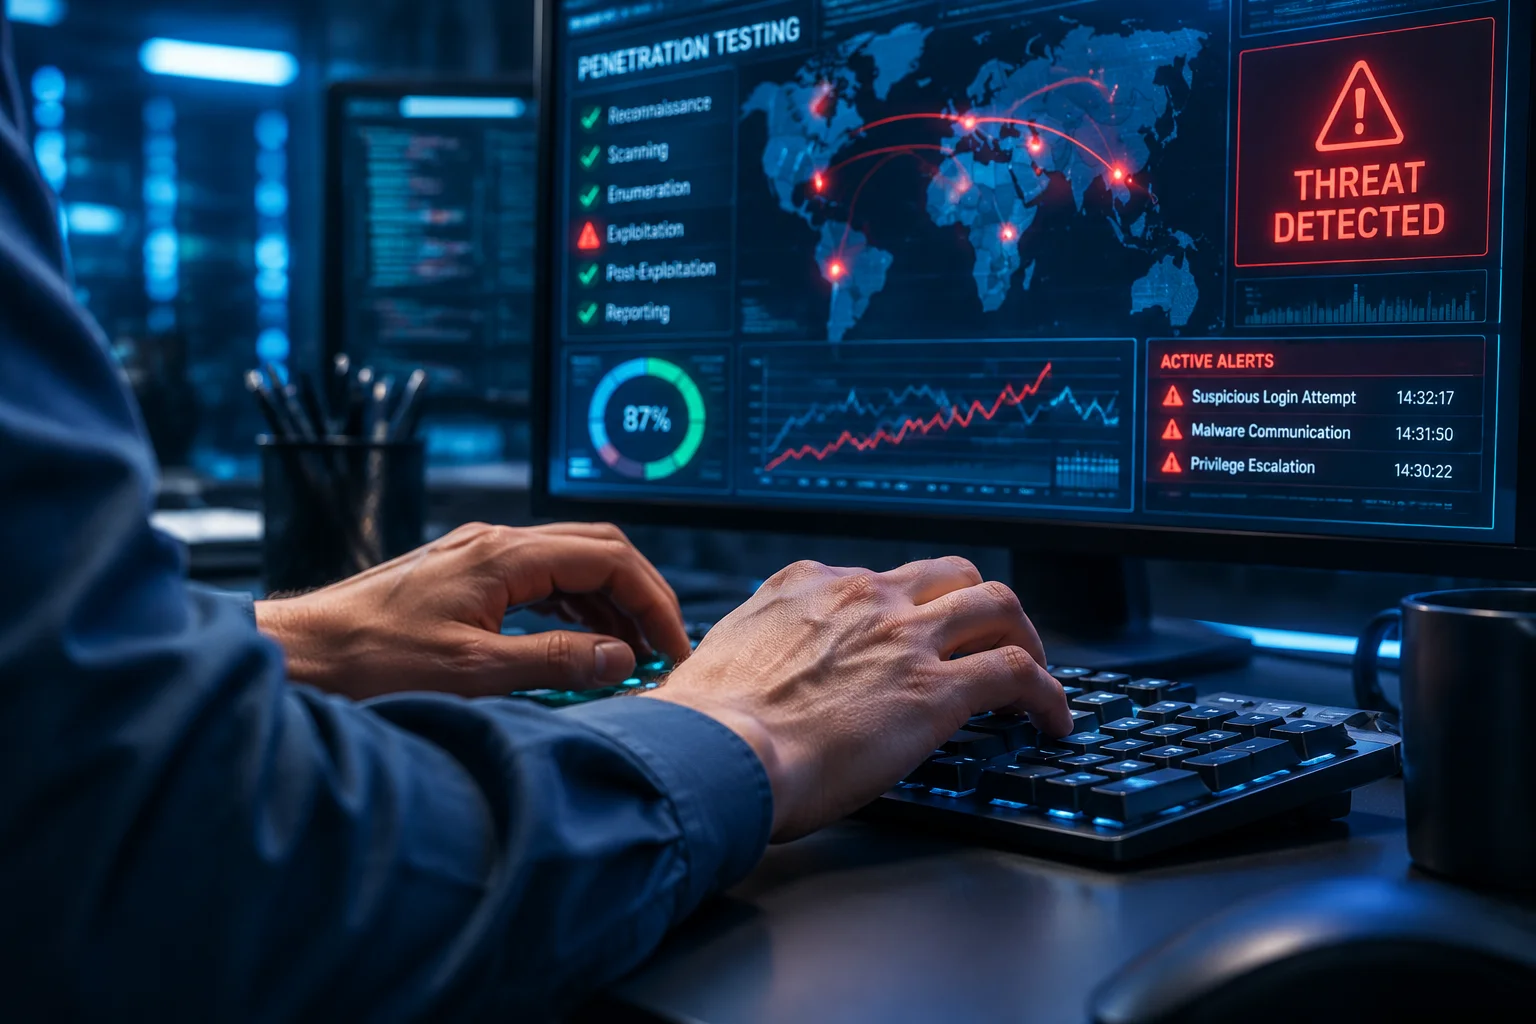
Penetration testing simulates real-world cyberattacks to measure how well an organization defends its assets against determined intruders. Ethical hackers use the same tactics, techniques, and procedures as malicious actors, targeting web applications, internal networks, and wireless systems. This process exposes the gaps between theoretical security policies and actual operational practices. Security teams receive actionable data rather than vague warnings, allowing them to fix high-risk flaws before real attackers exploit them.
Conducting these tests regularly transforms a reactive security posture into a proactive strategy. Instead of waiting for an incident to reveal a weakness, organizations discover and patch vulnerabilities during planned maintenance windows. This approach minimizes downtime and protects brand reputation. Knowing exactly where the defenses break down gives system administrators the clarity they need to allocate resources effectively.
Securing Code From the First Line
Building custom software without integrated security checks is like constructing a house without locks on the doors. Developers face immense pressure to deliver features quickly, which often leads to rushed code containing injection flaws, improper authentication handling, and broken access controls. Integrating security into the development lifecycle ensures that software remains resilient against attacks from its initial release. Every API endpoint, database query, and user input field must be rigorously validated and tested.
- Static code analysis detects syntax and structural flaws early in the build cycle.
- Dynamic application testing evaluates running software under simulated attack conditions.
- Dependency scanning flags outdated third-party libraries carrying known vulnerabilities.
- Manual code reviews by security experts catch subtle logical flaws missed by automated tools.
- Continuous integration pipelines block insecure code from reaching production servers.
Fixing a vulnerability during the design phase costs a fraction of what it takes to remediate a breach after deployment. Software development teams that embrace secure coding practices protect their users and reduce long-term maintenance overhead. Quality code is secure code, and security cannot be treated as an afterthought tacked on right before launch.
Transforming Employees Into the First Line of Defense
Technology alone cannot stop a targeted social engineering attack. Cybercriminals routinely manipulate human psychology, bypassing advanced technical controls by tricking employees into revealing credentials or transferring funds. Corporate employee security training bridges this gap by teaching staff how to recognize phishing emails, suspicious phone calls, and physical tailgating attempts. When employees understand the risks, they stop treating security policies as corporate red tape and start acting as active guardians of company data.
Effective training programs move away from once-a-year slide presentations and incorporate interactive phishing simulations, practical workshops, and memorable real-world examples. Employees learn to pause and verify unusual requests rather than clicking links out of habit. Building this security-conscious culture takes time and consistent reinforcement, but the payoff is immense. A well-trained workforce neutralizes one of the most common vectors for unauthorized network access.
Cybersecurity is an ongoing process rather than a destination you reach and abandon. As infrastructure evolves and new threats emerge, organizations must continuously adapt their defenses, audit their systems, and educate their people. Staying ahead of attackers requires vigilance, technical expertise, and a willingness to confront uncomfortable security truths before someone else exploits them.
Comments
"The penetration testing team found critical flaws in our web application that we had completely missed. Their report was thorough, practical, and helped our developers patch the holes immediately."
Piotr Kowalski
"Custom software development used to be a headache for us until we partnered with this team. They built our new platform securely, on schedule, and without any hidden technical debt."
Katarzyna Wiśniewska
"We brought them in to run infrastructure audits and train our staff. The phishing simulation opened a lot of eyes around the office. Highly professional service from start to finish."
Tomasz Nowak
"The employee security training sessions were engaging and far from boring. Our team actually learned how to spot social engineering attempts in their daily email inbox."
Agnieszka Wójcik